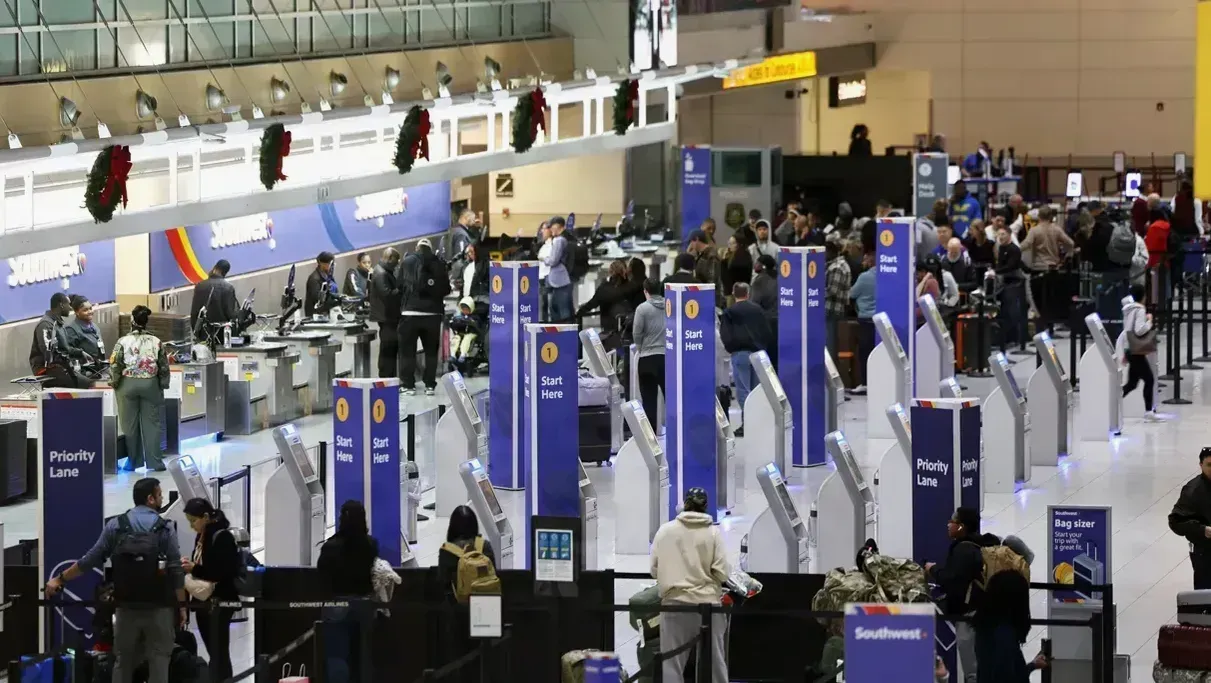
The United States has been rocked by a series of disruptive technology failures recently, ranging from grounded flights to frozen bank accounts, leaving many to wonder if these glitches are mere accidents or something more sinister. While government officials insist there is no evidence of foul play, some experts believe the chaos reveals dangerous cracks in the foundation of the country’s most vital systems. Dr. Ram Dantu, the founding director of the Center for Cyber and AI Security at the University of North Texas, warns that these events could be providing a roadmap for foreign adversaries looking for ways to dismantle American infrastructure.
Dr. Dantu noted that while network congestion or simple software bugs often cause such outages, it is impossible to rule out a calculated cyberattack entirely. He explained that sophisticated malicious software can sit dormant within a network for months or even years, spreading silently until an external actor decides to activate it remotely. This stealthy approach makes it difficult to distinguish between a routine technical failure and a targeted strike designed to cripple power grids, water supplies, or telecommunications networks.
Adding to his suspicion is the peculiar timing of some of these disruptions. According to Dantu, standard engineering practice dictates that major system upgrades happen overnight or in phased stages to avoid peak usage hours. Seeing critical updates occur in the middle of the business day struck him as highly unusual and potentially indicative of deeper issues beyond simple maintenance errors. For him, every public failure acts as a signal to enemies abroad about where the U.S. is most vulnerable.
Despite these warnings, top administration officials remain confident that the situation is under control. Secretary of State Marco Rubio stated clearly that federal investigators have found absolutely no evidence linking these separate incidents or connecting them to any foreign hacking group_or hostile government. Director of National Intelligence Jay Clayton echoed this sentiment, suggesting that typical security patches and routine upgrades are far more likely culprits than a coordinated campaign of digital warfare.